Business Compliance
CIS Controls v8, NIST Cybersecurity Framework (CSF)
A practical foundation for cybersecurity governance, risk reduction, and program maturity.
Governance, risk, and compliance support that helps you uncover gaps, meet customer and regulatory requirements, and stay audit-ready.
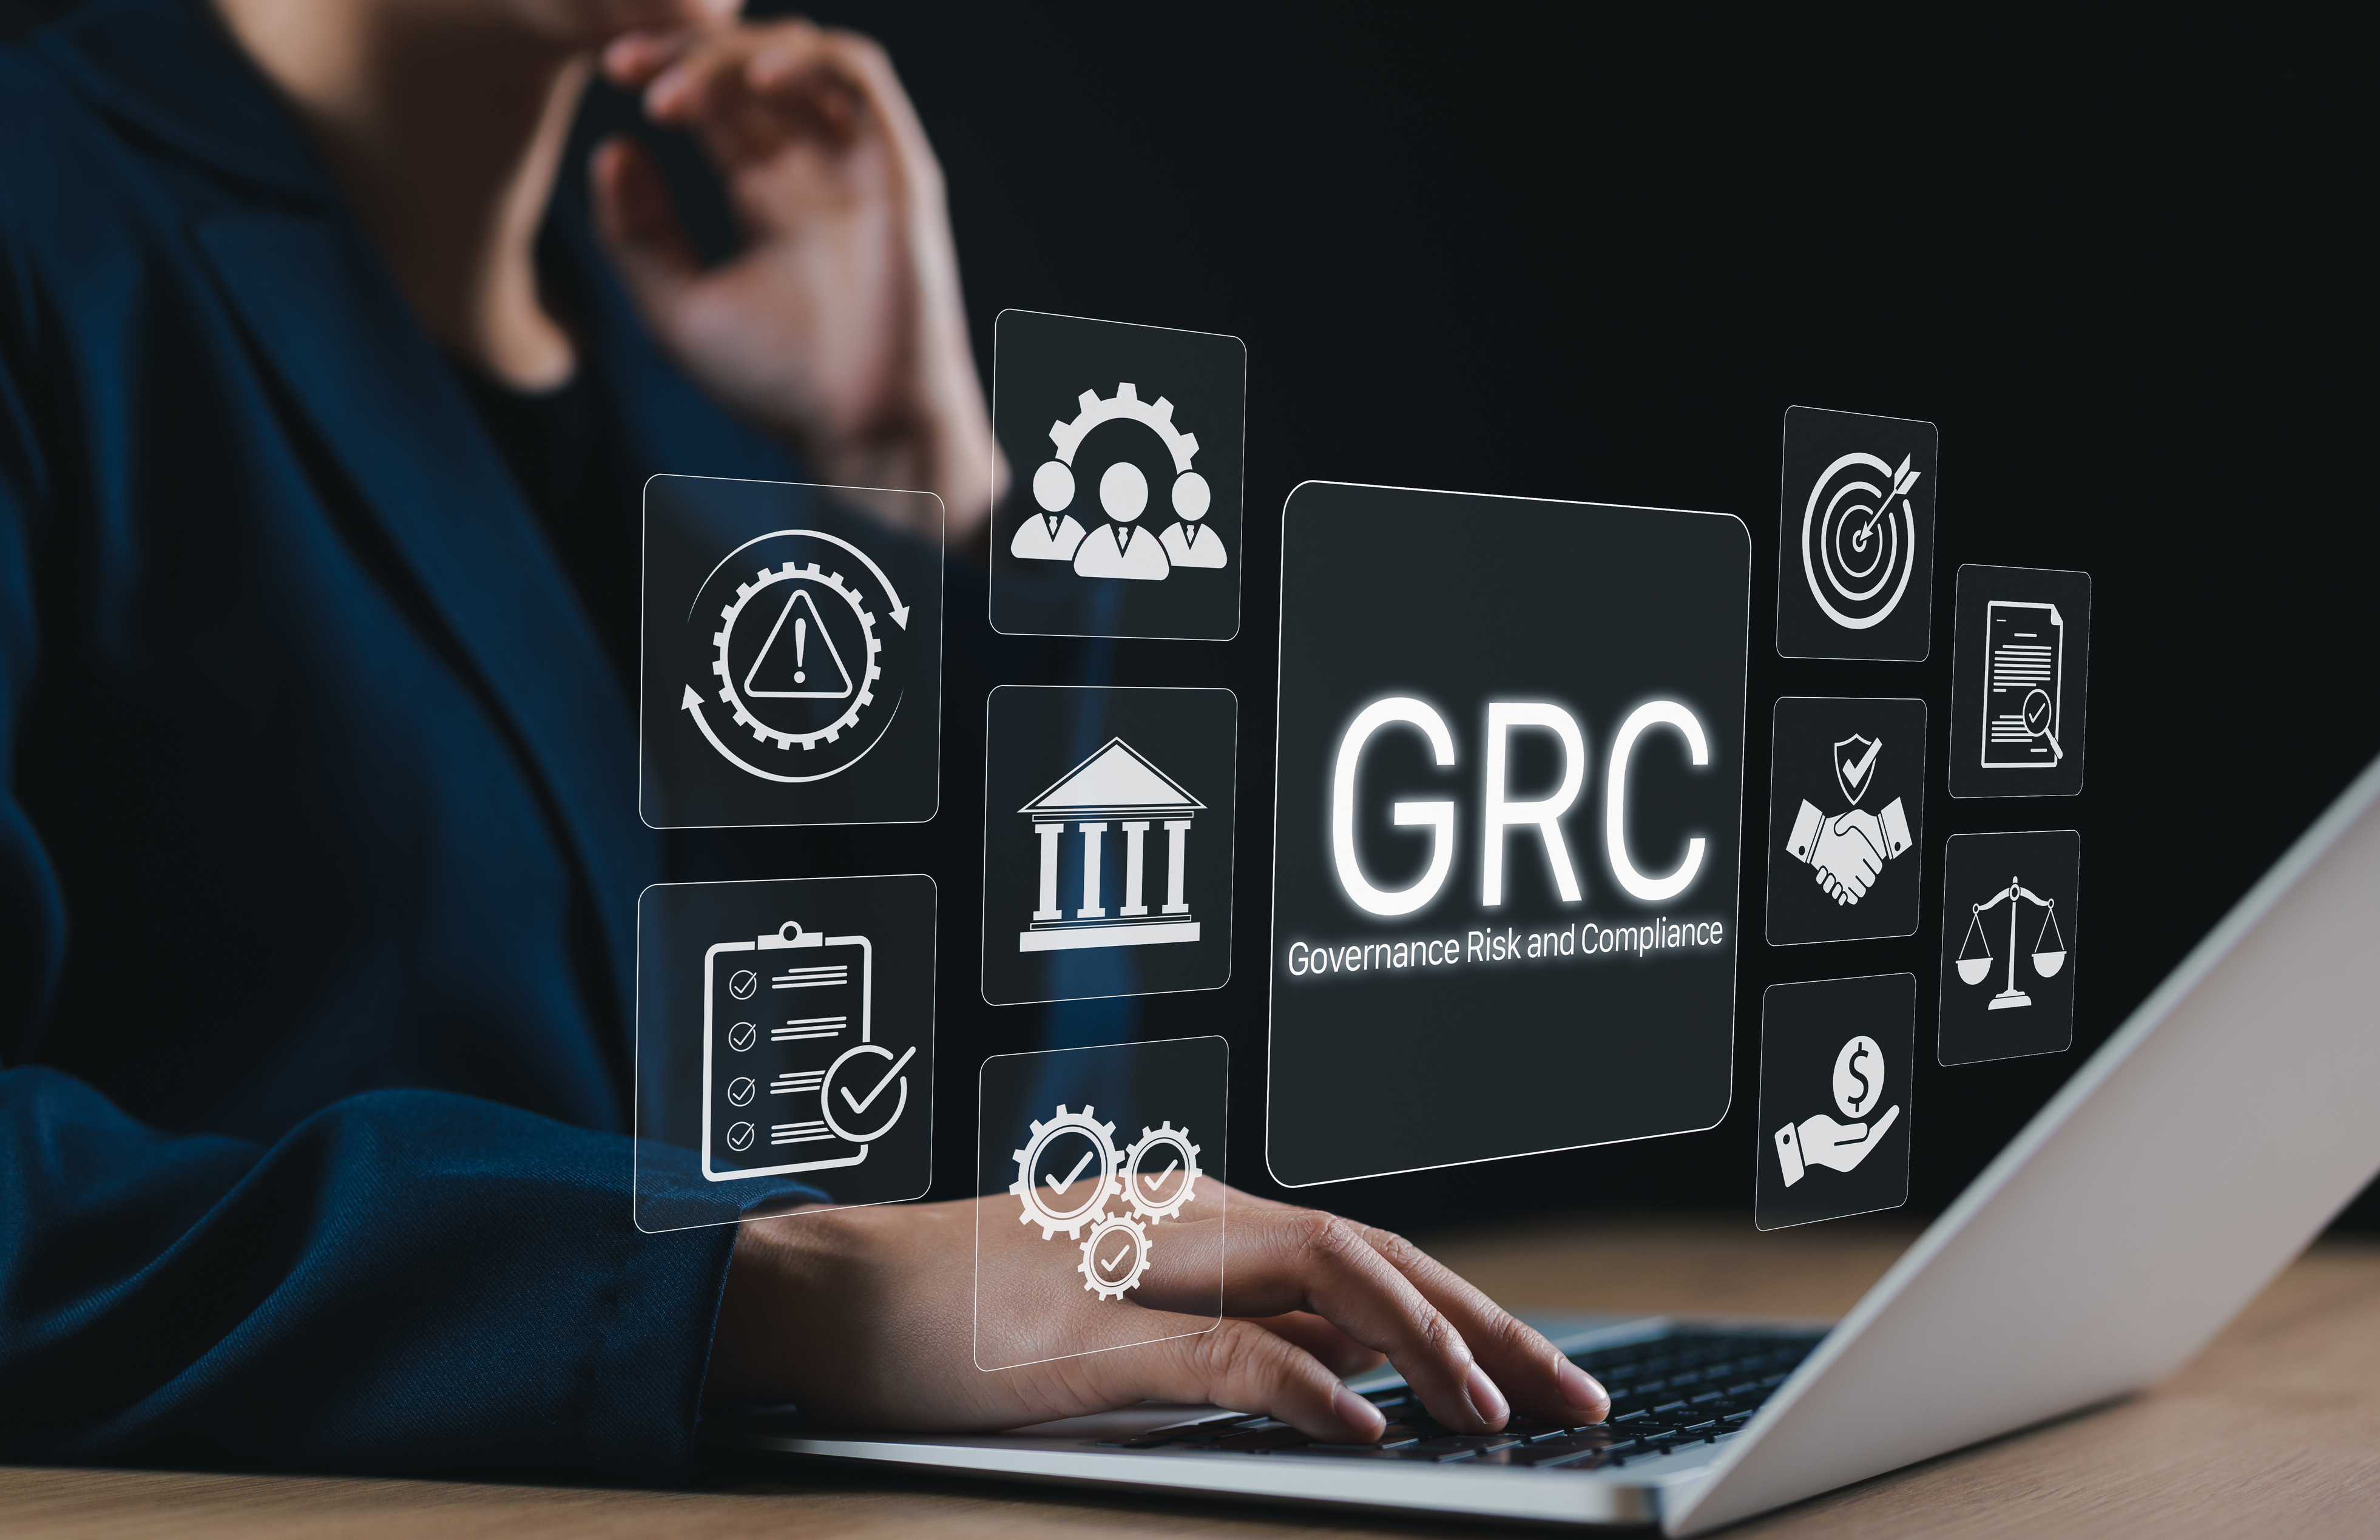
Governance, risk and compliance (GRC) services bring structure to how your business manages security, privacy and regulatory obligations. Governance sets policies and accountability, risk management identifies and prioritizes threats, and compliance demonstrates that you meet the expectations of customers, insurers and regulators.
As cybersecurity risk grows, customers require vendors to complete security questionnaires and risk assessments, and cyber insurers expect more than an incident response plan. They want framework compliance tailored to your industry, state, and markets.
Our GRC team identifies applicable frameworks and state requirements, unconvers compliance gaps, builds a practical remediation plan, and creates an ongoing compliance program that grows with your business.
Whether you need a clear picture of your current risk or ongoing support to keep your compliance program on track, we meet you where you are and build from there.
Determining which frameworks apply to your business can be challenging. Here are the most common frameworks we help organizations meet, organized by type of compliance.
CIS Controls v8, NIST Cybersecurity Framework (CSF)
A practical foundation for cybersecurity governance, risk reduction, and program maturity.
NIST SP 800-171, CMMC
ProRequired for organizations supporting the Department of Defense and federal supply chains.
PCI DSS, GLBA, NYDFS
Address financial data protection requirements and regulatory oversight obligations.
SOC 2, ISO 27001, CCPA, GDPR
Meet the requirements of enterprise customers, procurement teams, and state regulations.
NIST CSF, CMMC, IEC 62443
Support cybersecurity resilience while meeting customer and defense contractor requirements.
SOX, COBIT
Strengthen internal controls and governance to meet public company reporting requirements.
A strong GRC program does more than check boxes. It protects revenue, builds trust, and keeps your business ready for what’s next.
Demonstrate compliance with the regulations and standards that apply to your business.
Follow a clear roadmap that matures your security program as you grow.
Meet customer and supply chain security expectations with confidence.
Improve accountability with clear policies, ownership, and oversight.
Support renewals and questionnaires with documented, defensible controls.
Stay prepared for audits and customer reviews at a moment’s notice.
Give leadership a recurring, easy-to-understand view of your risk posture.
Meet the security requirements that come with new contracts and partnerships.
No confusing jargon. Just clear guidance with outcomes.
Choose the services you need and scale as you grow.
Make informed IT decisions that reduce risk and control costs.
Clear expectations, no overpromising, and results you can measure.
Get answers to the most common questions we hear from businesses building or improving their compliance programs.
It depends on your industry, the data you handle, and who you do business with. For example, government contractors often need CMMC or NIST 800-171, healthcare organizations need HIPAA, and SaaS providers are frequently asked for SOC 2. Our team helps you identify the framework that delivers the most immediate value, then build on it.
A security risk assessment is a point-in-time evaluation that identifies gaps and gives you a prioritized path forward. GRC as a Service is an ongoing program that keeps policies, plans, vendor reviews, and reporting current throughout the year so you stay audit-ready.
Many businesses start with a security risk assessment to understand where they stand today. From there, we help you choose the right framework and level of ongoing support based on your goals, customer requirements, and budget.
Yes. Documented policies, tested incident response plans, and current risk assessments make cyber insurance questionnaires easier to complete and can help you identify gaps in your coverage.
Not necessarily. Our GRC services provide access to experienced compliance professionals, including vCISO support, without the overhead of a full-time hire.
Talk with our GRC team about where your business stands today and the most practical path to becoming audit-ready.